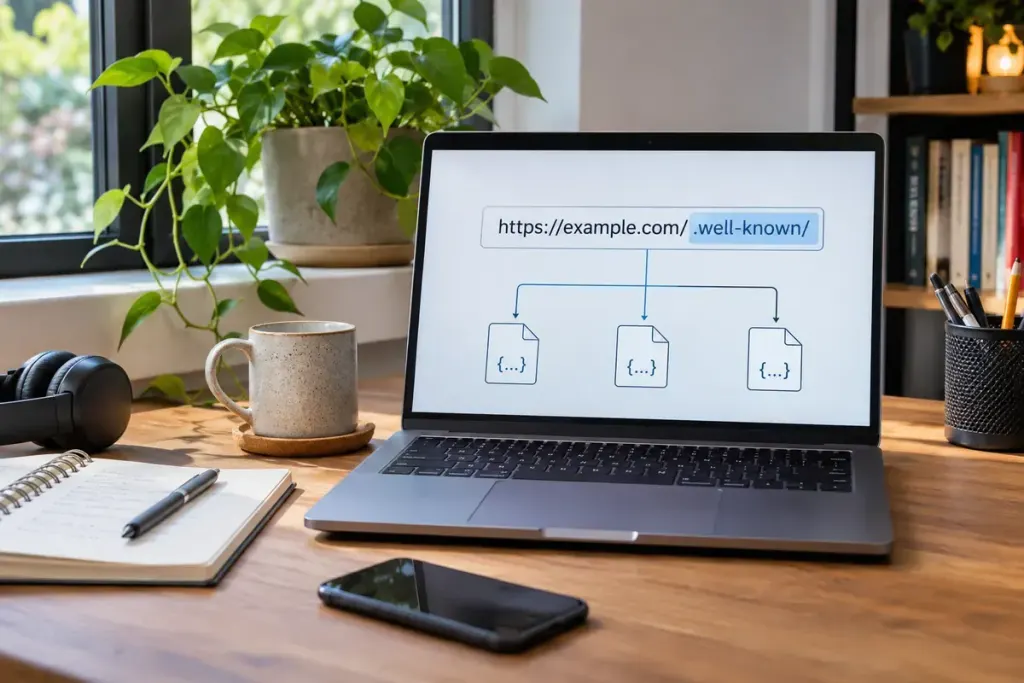
A security contact file and a service-discovery document may both appear under a website’s /.well-known/ path. The shared location is a convention for finding particular information, not a special folder that makes any file inside it authoritative.
RFC 8615 defines well-known URI locations and a registration approach. The idea is to give a standardised service a predictable place to look, avoiding a different discovery path on every participating site.
The suffix supplies the meaning
The directory name alone tells you little about the document. A registered suffix and its defining specification explain the expected format and use. A client still needs to follow the rules for that particular service, including any relevant origin or transport requirements.
For a simple analogy, a building may reserve one noticeboard for official notices. The board’s location helps you find them, but you still need to read who issued a notice and what it actually says. A predictable path solves a discovery problem; it does not settle every trust question.
Check the origin as well as the path
If someone sends you a link ending in a familiar well-known filename, inspect the hostname. An unrelated site can copy a path. The presence of those characters does not prove affiliation with the organisation you intended to reach.
For a site operator, check the defining standard before adding a new file. Confirm the content type, syntax, update process and any expiry or contact requirements it specifies. Keep responsibility for maintaining the document clear, because a once-correct endpoint can become stale.
A useful test begins with the complete URL and the expected response, not just whether a browser shows something. Record redirects and unexpected HTML error pages as well as the status code.
The convention is valuable precisely because clients can recognise a shared arrangement. Use that predictability carefully: find the right location, verify the right origin, and interpret the content according to the standard that gives it meaning.