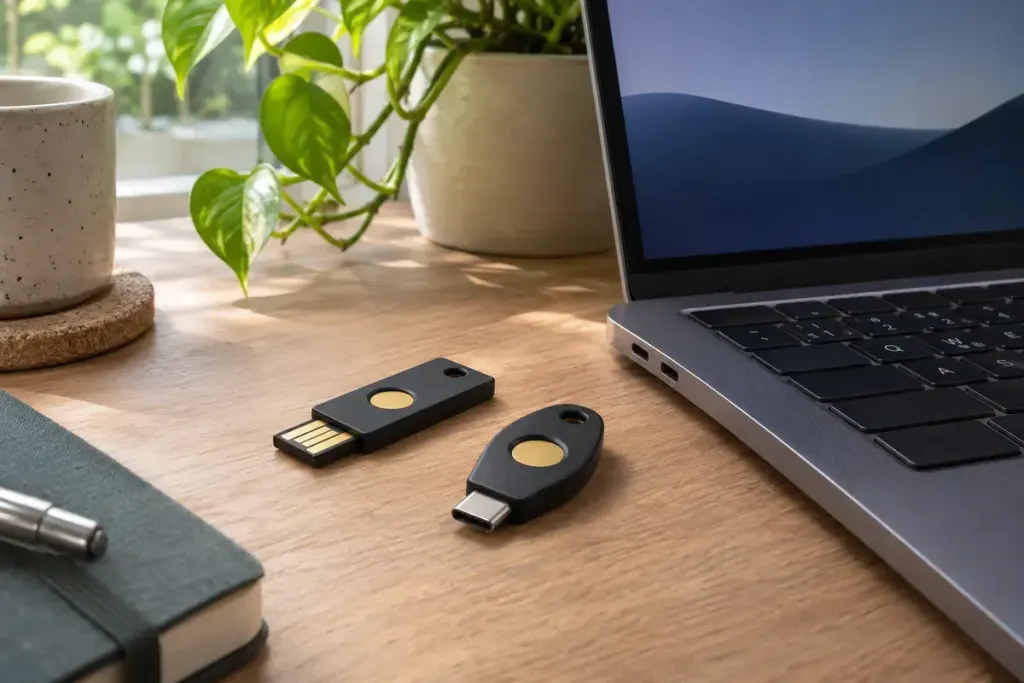
You insert a hardware security key to sign in, and a prompt asks for its PIN. Entering the website password may feel natural, but it can be the wrong credential. A FIDO2 PIN belongs to the authenticator, not to each online account using it.
Understanding that distinction is especially useful when a key has been registered with several services.
Identify which prompt you are seeing
Yubico’s FIDO documentation explicitly distinguishes the authenticator’s local PIN from a password. A website account password, a computer sign-in PIN and a hardware key’s FIDO2 PIN can be separate things.
Read the prompt and confirm that you initiated the sign-in on the correct site. Do not type a key PIN into an arbitrary web form that claims to need it for “verification.” Use the platform’s supported security-key flow.
Repeated guessing has consequences
The Yubico retry documentation describes limits on incorrect attempts and the consequences of blocking the FIDO application. Exact behaviour depends on the authenticator, so consult its current documentation rather than assuming unlimited tries.
If you are unsure, stop and identify which key and PIN were set up. An illustrative mistake is to cycle through old website passwords because the prompt appears during a website login. That does not make those passwords candidates for the key’s local PIN.
Check recovery before resetting
A FIDO reset can remove credentials from the authenticator. Before taking that step, establish which accounts depend on it and whether another registered key, recovery method or organisational help desk is available.
Keep recovery information according to each service’s guidance and store it securely. Do not send PINs, passwords or recovery codes to someone offering to “check” the key.
For future setup, record which authenticator is registered with which accounts without writing secrets into a public inventory. Clear labels and a tested recovery route are more useful than trying to remember, during a lockout, which of several similar prompts you originally configured.