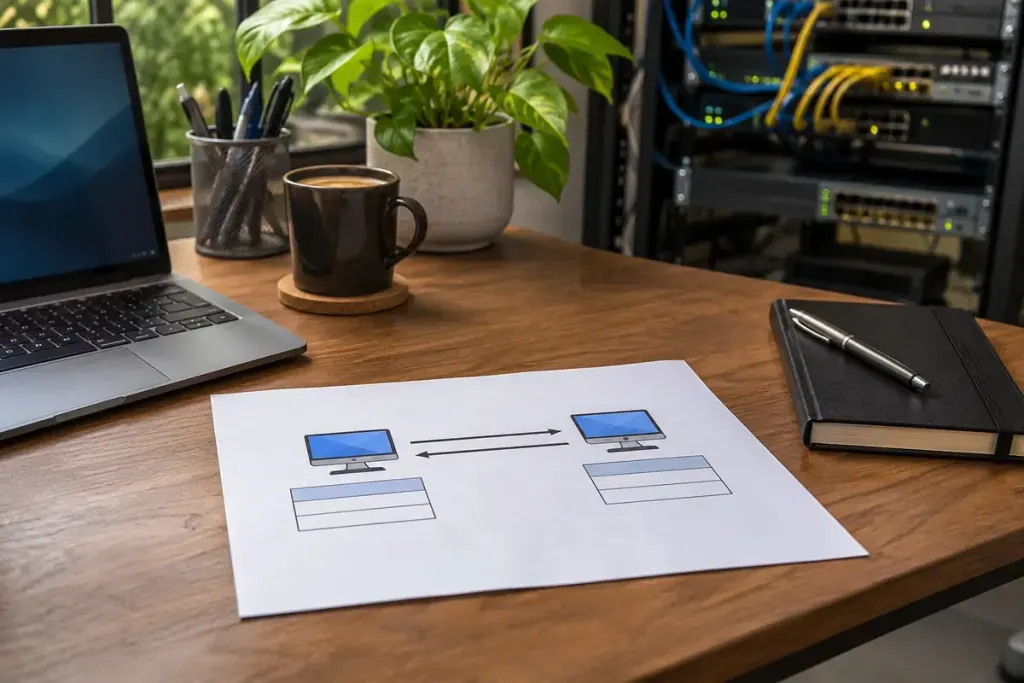
Typing a website name asks one kind of DNS question. Starting with an IP address and asking for a name asks another. Reverse DNS is not simply the original lookup played backwards through the same record.
A forward lookup commonly uses an A or AAAA record to associate a name with an address. A reverse lookup asks for a PTR record in the relevant reverse-DNS namespace. The records can be administered through different arrangements.
Cloudflare’s documentation on reverse zones and PTR records explains the role of control over the IP address space. Owning a domain name does not necessarily give you control of the reverse record for an address supplied by a hosting company.
Why the answers may not form a perfect pair
One server address can support several websites. A reverse result may identify a hosting or mail-server name rather than the website you expected. Conversely, an address may have no useful PTR response at all.
Those observations are not, by themselves, evidence that a website is fraudulent or that the connection is unsafe. DNS naming, certificate validation and the trustworthiness of the organisation are different questions.
For a simple learning exercise, compare a forward lookup and a reverse lookup on an address you are authorised to inspect. Record the queried name or address, the result and the time. Do not turn one mismatch into a security verdict.
When you need a record changed
Ask the provider responsible for the address allocation how reverse DNS is managed. Supply the exact IP address and intended hostname through their normal support or control-panel process. Check that the forward record is also configured appropriately for the service.
Keep the purpose clear. A mail-service setup may have requirements that are not relevant to an ordinary website, and a provider may impose its own validation rules. Follow the documentation for the actual service rather than copying an unrelated server’s name.
If a change takes time to appear, note the previous answer and its caching context before making repeated edits. The useful mental distinction remains the same: a domain-to-address record and an address-to-name record are related pieces of configuration, not one automatically reversible entry.