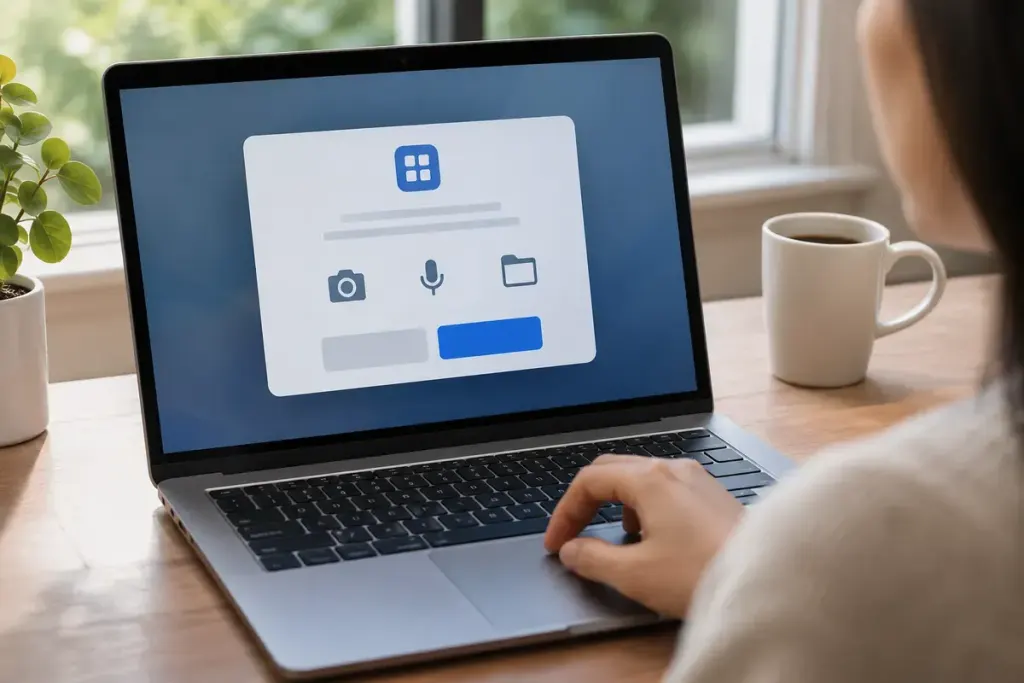
A sign-in page can be genuine while the request behind it is unsafe. In consent phishing, an attacker persuades someone to authorise an application to access account data. The attacker may not need to collect the password if the user grants the requested permissions.
That is why checking the login domain, while important, does not finish the decision. You also need to understand which app is asking, what it wants and why the request appeared.
Read the permission as a continuing relationship
Microsoft’s guidance on consent phishing explains how malicious applications can abuse user consent. Depending on the grant, an app may receive access to information or actions beyond the immediate sign-in.
Compare the permission with the task. A simple calendar utility asking for broad mail access deserves a pause. A familiar-looking app name is not sufficient evidence that the application is the one your organisation approved.
Check the request through a route you already trust
If an unexpected message asks you to approve an app, do not use the message itself as the proof of legitimacy. Open the service or your organisation’s software catalogue independently, or ask the responsible administrator. Describe the app and permissions without sending account secrets.
For a work account, an approval process may exist precisely because the consequences extend beyond one person’s inbox. Do not work around that process by switching to another account or asking a colleague to approve the same request.
If you already approved something suspicious
- Report it promptly through the account provider’s or organisation’s official security route.
- Record the app name, approximate approval time and message that led to it.
- Review and revoke the suspect application’s access through the appropriate account controls, with administrator help where needed.
- Follow the resulting advice about sessions, credentials and possible data exposure.
A password reset alone may not remove an existing application permission or every issued token. The permission grant needs its own investigation. Conversely, revoking access does not prove that information previously accessed has been recovered.
For administrators, the practical lesson is to govern application consent, restrict unnecessary permissions and review unused or suspicious grants. For everyday users, the key pause is short: “I recognise the sign-in service, but do I recognise and need this app’s access?”