You follow a link from one website to another. Depending on the policy and circumstances, the next request may include information about the page you came from. Referrer-Policy helps determine how much of that referring address is sent.
MDN’s Referrer-Policy reference describes the response header and related HTML controls. The request header is historically spelled Referer, while the policy name uses the ordinary double-r spelling.
An origin is smaller than a full address
Consider an invented address, https://example.com/guides/packing?view=short. Its origin is https://example.com. A policy that sends only the origin leaves out the path and query, while no-referrer suppresses the referring information entirely.
The common strict-origin-when-cross-origin policy distinguishes same-origin requests from cross-origin requests and also treats a move from HTTPS to HTTP differently. Read the policy’s full definition rather than assuming every click produces the same header.
Observe it with harmless test pages
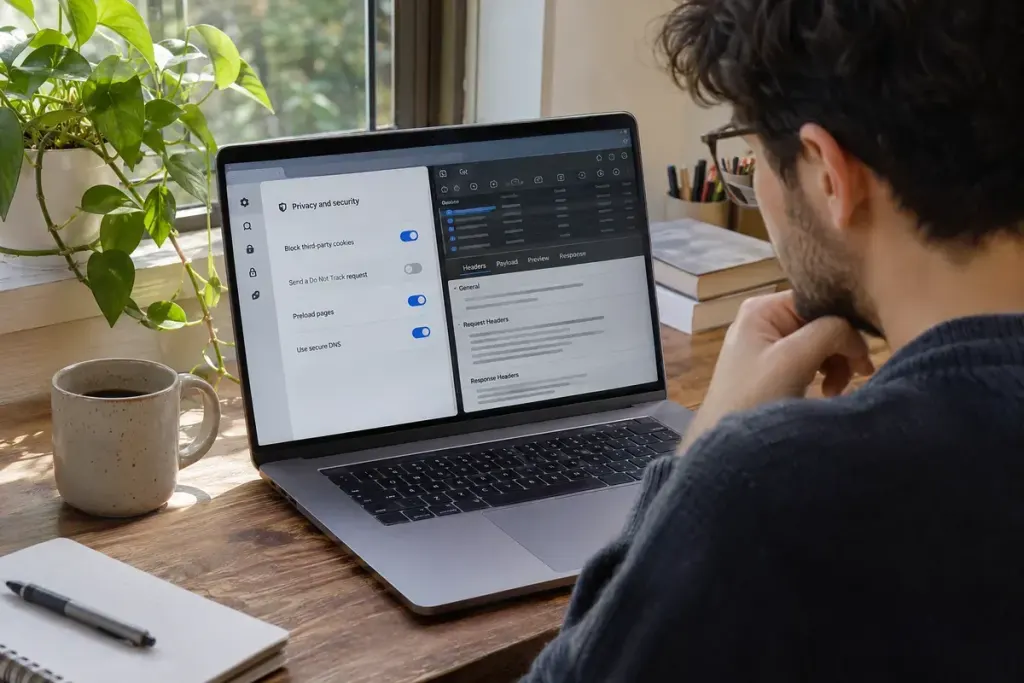
If you maintain a site, use a controlled test page and the browser’s network tools to inspect the actual request. Try an internal link and a link to another origin. Keep the browser version and policy setting in your notes.
Do not put passwords, tokens or real personal details into the test address. A referrer policy is not a reason to place secrets in URLs in the first place, and it does not control every possible way an application can transmit information.
A practical comparison records the source origin, destination origin, policy and observed header. That makes a difference between two tests explainable without relying on an assumption about the browser default.
For everyday browsing, a missing referrer is not proof of anonymity. The destination may still receive cookies, account information or other request data. This policy has a specific job: limiting one route by which details of the referring address travel.