Software and Security
A security report is easier to act on with one reproducible example
Write a useful vulnerability report with authorised scope, a minimal reproduction, observed impact and evidence that avoids exposing private data.
Practical security for everyday technology.
Write a useful vulnerability report with authorised scope, a minimal reproduction, observed impact and evidence that avoids exposing private data.
Understand USB selective suspend before changing power settings, and collect useful observations when an idle device fails to respond.
CHIPS partitions a cookie by the top-level site. Understand what that changes for embedded services without treating it as complete anonymity.
Some websites keep loading without a connection because a service worker saved resources. Learn what offline access does—and does not—tell you about a site’s data.
Persistent browser storage can protect site data from automatic eviction, but it is not a backup. Check what an offline app can export before relying on it.
Browser site isolation adds boundaries between website content. Understand why process counts do not map neatly to tabs and what this protection cannot do.
An app sandbox restricts what software can reach, while permissions and the information you provide still shape privacy risk.
WebAuthn attestation concerns an authenticator’s provenance during registration. Separate it from the proof used at sign-in and consider the privacy trade-off.
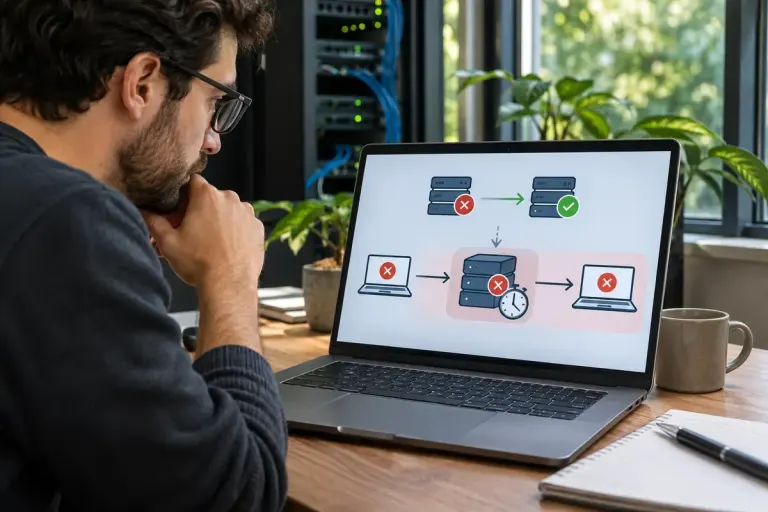
A newly created DNS record can still appear absent because a resolver cached an earlier negative answer. Learn what to check before changing it again.